VICTOR SOLUTIONS / PUBLIC SECTOR
Run without a connection to the outside world.
Every Victor edition installs, upgrades, activates and runs air-gapped. Enterprise adds the identity, audit and evidence controls regulated missions ask for.
Air gap in every edition · no certification or ATO claimed01 / DELIVER AND OPERATE
One signed bundle across the boundary.#
The air-gap bundle carries images, the Helm chart, binaries, a Terraform provider mirror, SBOMs, documentation and the public signing key. It expires, one year by default, so stale media does not linger.
- Verify
victor-load checks the bundle’s signature and every image before anything is loaded.
- Load
Push images to the site registry. victor-load writes Helm values that reference each image by digest.
- Install
Install with Helm or Zarf. Victor’s air-gap test checks that an install makes no DNS lookups outside the cluster.
- Activate
Enterprise licenses are signed files activated offline. A license never stops VMs or running automation.
victor-load verify victor-<v>.tar
victor-load push --registry registry.enclave.internal:5000 victor-<v>.tar
Supply chain evidence
Images are minimal, built for amd64 and arm64, signed with cosign and carry CycloneDX SBOMs. The release build fails on any unaccepted high or critical scanner finding in an image.
02 / POLICY ON THE SCREEN
Notice and marking, from the first page.#
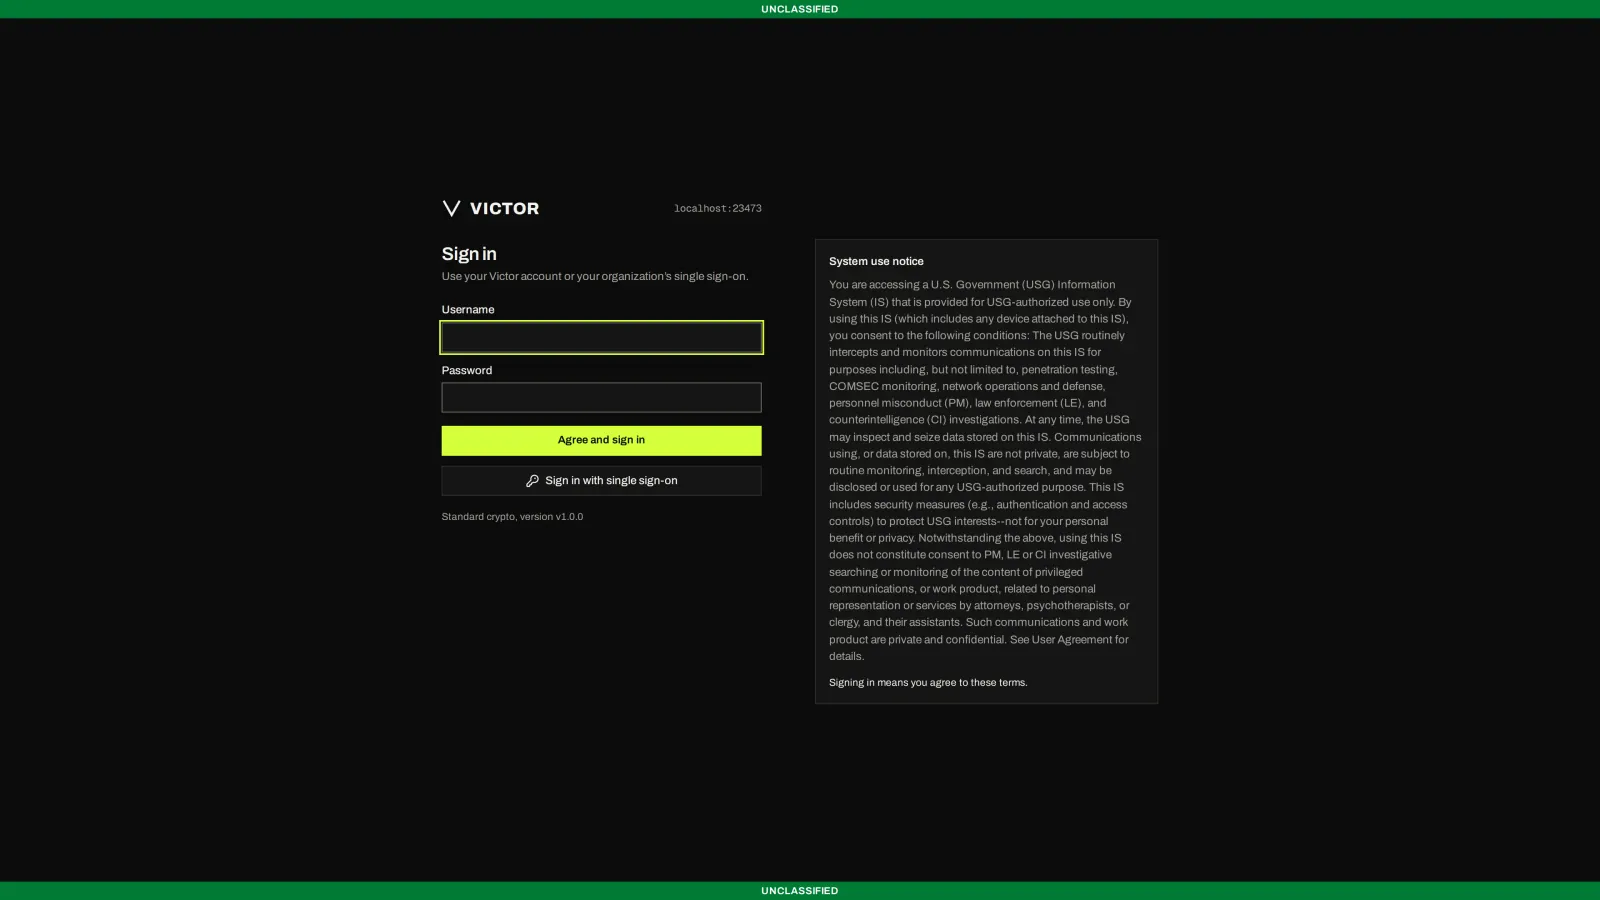
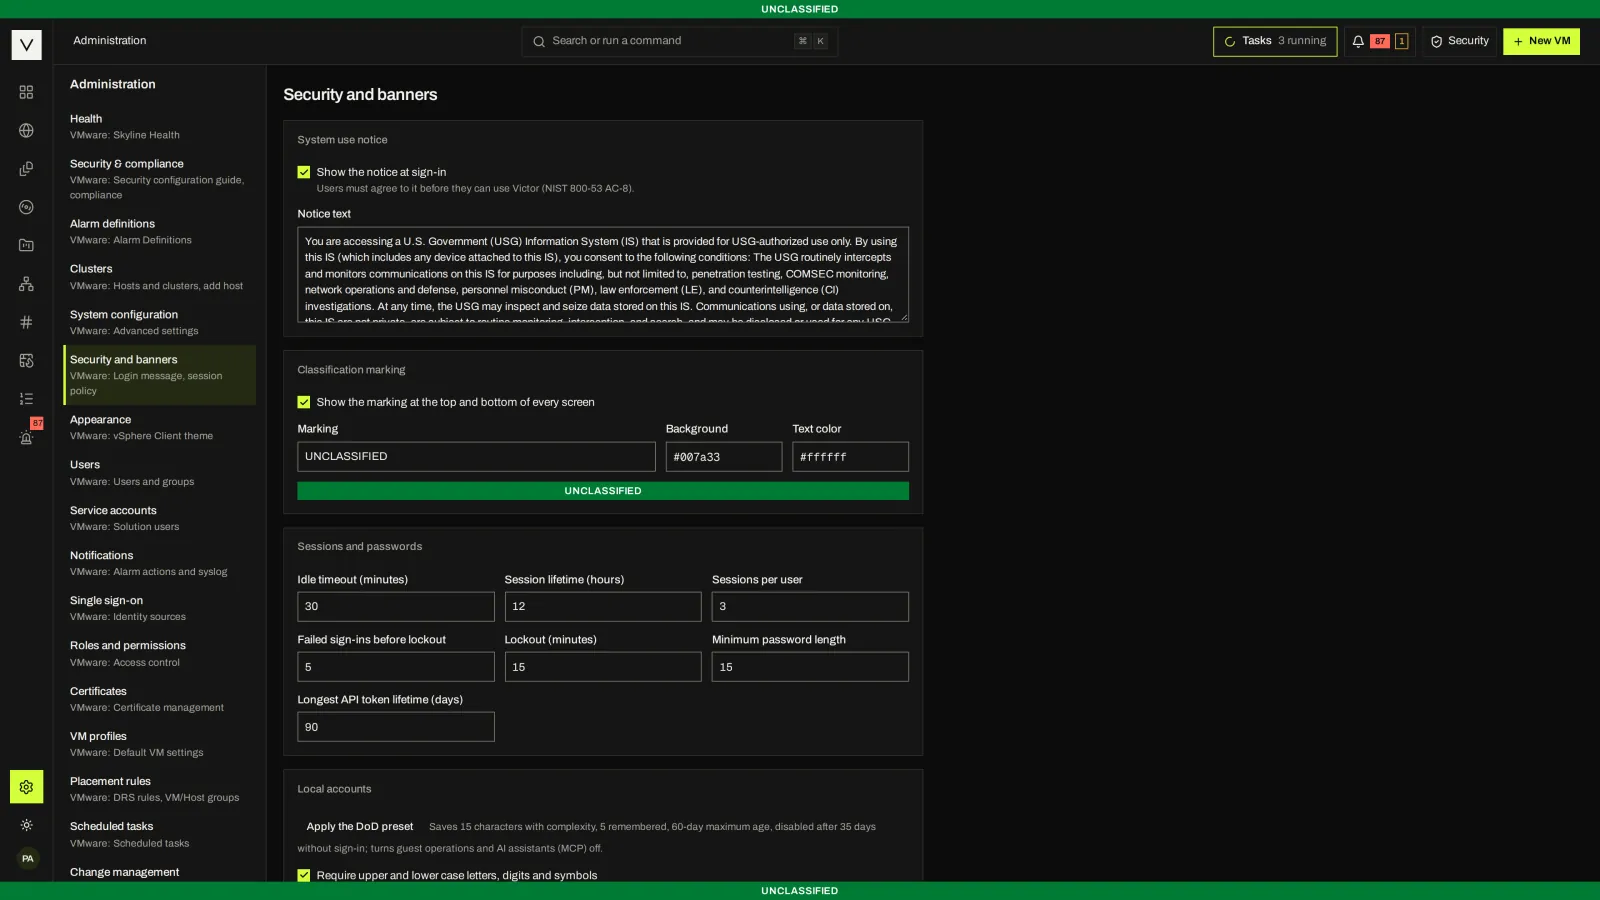
Every edition can show a consent notice before sign-in and a classification banner at the top and bottom of every page. Enter the USG notice text in the consent setting. Enterprise’s DoD preset applies the DoD account policy in one step and turns guest operations and the MCP server off.
Session limits, password policy and lockout settings are standard and visible in the Security & Compliance Center.
03 / WHAT EACH EDITION BRINGS
Built for the assessment, too.#
| Need | Community | Enterprise adds |
|---|---|---|
| Disconnected delivery | Signed, expiring air-gap bundle; Zarf package; offline Host ISO | Enterprise builds and bundles |
| Identity | Local accounts with TOTP or security keys, OIDC, LDAP/AD | CAC/PIV over mutual TLS with CRL and OCSP |
| Notice and marking | Consent notice, classification banner, account policy | DoD account-policy preset (passwords, inactivity, guest operations and MCP off) |
| Audit | Hash-chained log with signed checkpoints; syslog, webhook, email, Loki | Fail-closed audit; Splunk HEC |
| Evidence | Security & Compliance Center mapped to NIST SP 800-53; signed evidence package | OSCAL component definition and DISA STIG Viewer checklist |
| Cryptography | FIPS build mode you compile | Signed FIPS-mode release builds (validated-module pinning open) |
| Hosts | CIS AlmaLinux 9 Level 1 scans; management firewall | STIG profiles |
04 / BE PRECISE ABOUT ASSURANCE
What we do not claim.#
A FIPS-mode build is not a FIPS 140-3 validated configuration. The checks support NIST controls; they do not certify a deployment. Victor has no FedRAMP authorization, published STIG from DISA, third-party penetration test or published Accessibility Conformance Report today.
We would rather give your assessor the evidence and the open items than a badge.
Bring your boundary.
In a guided review we will walk through the evidence package, the audit chain and current open items against your control set.
Request a reviewFAQ
Mission questions.#
How do updates work without internet?
Bring the next signed bundle across the boundary, verify and load it, and upgrade with Helm. Victor Host updates the whole host image and can roll back. #
Do smart cards work directly in the browser?
CAC/PIV uses mutual TLS, so the browser presents the certificate. Reading PKCS#11 smart cards directly from victorctl is not supported yet; victorctl can use a client certificate. #
Does anything phone home?
No. victorctl has no telemetry and licenses activate offline. Victor’s air-gap test installs the bundle on a cluster with no route out and fails if any outside name is looked up, and victord logs every outside endpoint it will contact at startup. #
NEXT STEP
Review the controls with your team.
Bring your deployment boundary, identity requirements and evidence needs to a guided Enterprise demo.